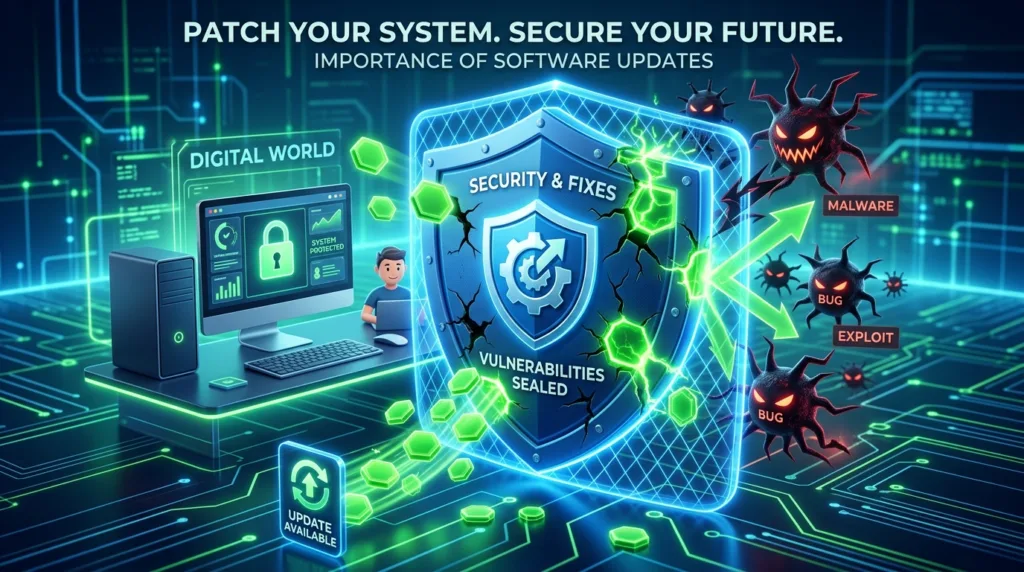
Software updates have an unfortunate reputation for arriving at exactly the wrong time.
You are about to shut down your laptop and Windows wants to install something. Your phone says an update is ready when the battery is already low. A browser restarts and several tabs disappear for a moment. Because the device seems to be working normally before the update, postponing it can feel harmless, particularly when the description mentions vague phrases such as “security improvements,” “bug fixes,” or “stability updates.”
The problem is that many of the most important changes inside an update are invisible precisely because they are designed to correct weaknesses before you personally notice them.
Software is extraordinarily complex. Operating systems, browsers, communication apps, cloud tools, media players, and other programs contain millions of lines of code that must interact with hardware, networks, files, and other applications. Even with extensive testing, flaws are discovered after software reaches users. Some cause ordinary bugs; others create security vulnerabilities that could allow an attacker to access information, bypass a protection, run unwanted code, or interfere with the way the software behaves.
When a developer fixes one of those weaknesses, the correction is often delivered through an update. Until that update reaches your device and is actually installed, however, the existence of the fix does not necessarily help you.
That gap between a vulnerability being known and your device receiving the correction is one of the clearest reasons software updates matter for digital security.
A security update is often a repair, not a new feature
People naturally notice updates that change something visible. A redesigned menu, a new camera feature, or a different icon makes it obvious that the software has changed, whereas a patch that modifies how the operating system handles a particular type of file may leave the interface looking exactly as it did yesterday.
From a security perspective, that invisible change can be much more important.
Imagine that researchers discover a flaw in the way a browser processes certain web content. Under the right conditions, a malicious page might be able to exploit that behavior. The browser developer investigates the issue, changes the relevant code, tests the fix, and distributes a new version. Once the corrected version is installed, that particular path of attack may no longer work in the same way.
If you continue using the older version, your browser may still contain the original weakness even though a correction is already available.
The Cybersecurity and Infrastructure Security Agency treats prompt software updating as one of its core everyday security recommendations. In its Secure Our World guidance on software updates, CISA specifically urges users to install updates promptly and enable automatic updates when possible, with particular attention to browsers and antivirus software.
That guidance reflects a simple reality: security is not finished when a developer creates a patch. The protection becomes useful to you when the corrected software is running on your device.
Updates can reveal something attackers did not know before
There is an interesting tension in the update process.
Before a security flaw is publicly documented, relatively few people may understand exactly how it works. Once a vendor releases a patch and publishes technical information about the vulnerability, defenders know what has been fixed — but attackers may also begin studying the difference between the old software and the new version.
This means that a newly released patch can sometimes create a race.
Users who update move onto the corrected version. Devices that remain on the older version may continue to contain a vulnerability whose existence has now become more widely known.
You do not need to understand exploit development or vulnerability research to see why indefinite delay can be problematic. If a security problem has been identified strongly enough that the manufacturer released a correction, keeping the vulnerable version simply because it still “works” is not the same as keeping a perfectly healthy version of the software.
That distinction is especially relevant for internet-facing software such as web browsers, operating systems, communication tools, and applications that routinely open files or content from outside sources.
“My computer is working fine” does not tell you whether it is secure
Many security problems do not announce themselves through obvious symptoms.
A laptop can start normally, connect to Wi-Fi, open documents, and stream video while still running software with known vulnerabilities. Security is partly about what the software would allow under unusual or hostile conditions, not only about whether it performs everyday tasks correctly.
This is why waiting for something to “feel wrong” before updating is unreliable.
A bug that causes an application to crash is noticeable. A vulnerability that could be exploited only after opening specially crafted content might remain completely invisible during months of ordinary use.
Microsoft makes this distinction clear in its Windows support documentation. The company states that unsupported versions of Windows stop receiving security fixes and that continuing to use software without ongoing updates can increase exposure to viruses, spyware, and other malicious software. Microsoft also recommends keeping Windows, browsers, and applications current in its guidance for protecting PCs from unwanted software.
The lesson is broader than Windows: a device can function while becoming progressively harder to protect if the software running on it is no longer being maintained.
Not every update is equally urgent
Saying that updates matter does not mean every notification deserves identical treatment.
Some updates primarily introduce features, redesign interfaces, or improve compatibility. Others correct ordinary bugs. Security updates address vulnerabilities, and certain critical fixes may deserve faster installation because the weakness is serious or already being exploited.
For an everyday user, it is not always realistic to analyze the technical severity of each update individually. That is one reason automatic updates are useful: they allow routine security fixes to arrive without requiring you to evaluate a long list of technical advisories every week.
CISA recommends enabling automatic updates when available, while also noting that some updates still require user action. The practical benefit is less about convenience alone and more about reducing the period during which an available security fix remains uninstalled.
There are reasonable exceptions. A company may test updates before distributing them to thousands of employees because compatibility matters. Someone relying on specialized professional software may wait briefly to confirm that a major operating-system upgrade will not disrupt an essential workflow.
That is different from repeatedly pressing “Remind me later” for months because the update feels inconvenient.
A thoughtful delay has a reason and an endpoint. Indefinite postponement does not.
An update and an upgrade are not always the same thing
The terminology can create unnecessary confusion.
An update often refers to a relatively incremental change: security fixes, bug corrections, minor improvements, or changes delivered within the version of software you are already using.
An upgrade commonly refers to a larger move, such as installing a new major version of an operating system.
The exact vocabulary varies among companies, so the distinction is not universal. What matters is recognizing that keeping a device secure does not always require adopting every major redesign the moment it appears.
Apple, for example, recommends using the latest macOS version compatible with a Mac because current releases include security, stability, and compatibility improvements. Its official macOS update guidance directs users to Software Update for compatible updates and upgrades.
At the same time, software vendors may continue distributing security fixes to more than one supported version for a period. The details change over time, which is why the most reliable approach is to follow the vendor’s current support information rather than assuming an old version will receive patches indefinitely.
Security depends not merely on whether software is old but on whether that version is still actively supported.
End of support changes the situation
A device does not stop turning on the day its operating system reaches end of support.
This can make the transition deceptively easy to ignore.
The desktop still appears. Applications still open. Files remain where you left them. From the user’s perspective, very little may seem to have changed.
What changes is the relationship with the developer.
Microsoft explains this directly in its Windows support lifecycle guidance: an unsupported version no longer receives the normal stream of software updates and security fixes, even though the computer itself may continue functioning.
That is a fundamentally different situation from postponing one update for a few days. When a platform is no longer supported, newly discovered vulnerabilities may not receive the same ongoing corrections available on supported versions.
Eventually, that can affect more than security. Browser developers, application vendors, and hardware manufacturers may also reduce support for older operating systems, gradually making the device less compatible with current software.
For beginners, the useful question is not “Does this computer still work?” but “Is the software on this computer still supported?”
Those are not the same thing.
Browsers deserve special attention because they constantly process outside content
A web browser spends much of its life interacting with information you did not create.
Every website can contain scripts, images, video, fonts, documents, advertisements, and other resources that the browser has to interpret safely. That makes browsers a particularly important category to keep current.
If a browser developer discovers a vulnerability related to how certain web content is processed, an update can close that weakness before you encounter a malicious page designed to exploit it.
This is one reason CISA specifically highlights browsers when recommending prompt software updates.
Modern browsers often update automatically, which can make the process nearly invisible. You may occasionally be asked to restart the browser so the newest version can take effect, and postponing that restart indefinitely can leave the older code running longer than necessary.
If browser terminology itself is still unfamiliar, What Is a Web Browser and How Does It Work? explains how the browser sits between you and the websites you visit. Understanding that role makes it easier to see why its security matters so much.
Apps need updates too
It is easy to think of “software updates” as something Windows, macOS, Android, or iOS does, while treating installed applications as a separate matter.
They are not exempt from the same basic problem.
A messaging application can contain a vulnerability. So can a PDF reader, office suite, media player, cloud-storage client, game, browser extension, or utility installed years ago and forgotten.
Some programs update themselves automatically. Others receive updates through the Microsoft Store, Apple’s App Store, Google Play, or another trusted distribution system. Traditional desktop software may have its own updater built into the application.
The safest source for an update is generally the software’s own trusted update mechanism or an official store, not a random webpage claiming that your program is outdated.
This distinction matters because fake update warnings are themselves a common way of persuading people to install unwanted software. If an unfamiliar website suddenly announces that your browser desperately needs an update, close the page and check the browser’s own update controls instead.
How to Install and Uninstall Programs Safely covers the broader principle of obtaining software from sources you can identify rather than responding to whatever download prompt appears first.
Restarting is sometimes part of the update, not an optional annoyance
One reason updates are postponed is the request to restart.
Restarting interrupts work, closes applications, and creates uncertainty about how long the computer will be unavailable. Yet some updates cannot fully replace files or components while the operating system is actively using them, which is why the final stage may need to happen during a reboot.
Until then, parts of the update may be downloaded and prepared without the corrected code being fully active.
Microsoft’s Windows Update guidance tells users to restart when prompted so available updates can finish applying. Apple likewise notes that certain security-related background updates take effect only after a Mac restarts.
That does not mean you need to restart immediately in the middle of an important meeting. Modern systems generally provide scheduling options precisely because users need some control over interruptions.
What matters is completing the process within a reasonable period rather than allowing “Restart later” to become the permanent state of the machine.
A good practical habit is to save your work and install or finish updates at a natural stopping point: the end of the workday, before leaving for lunch, or whenever you know the device can remain unavailable briefly.
Security works better when it fits into routine rather than competing with it.
Updates are not a guarantee that nothing bad can happen
There is a danger in turning good security advice into absolute promises.
A fully updated computer can still be compromised if you enter credentials into a phishing page, install malicious software deliberately, approve an attacker’s sign-in request, or expose sensitive information in some other way. New vulnerabilities can also exist before a developer discovers and patches them.
Updating reduces a category of avoidable risk: continuing to run known vulnerable software when a correction is already available.
It should therefore sit alongside other habits rather than replace them. Strong, unique passwords protect accounts in a different way. What Is Two-Factor Authentication and Why Should You Use It? adds another layer when a password is compromised. How to Tell If a Website Is Safe to Visit helps with decisions that software alone cannot make for you.
No single measure is responsible for all of digital security.
That is precisely why easy protections are worth using: they remove vulnerabilities you do not need to leave open.
The useful question is not whether updates are annoying
They often are.
A large update can take time. An interface may change. A restart can interrupt something you were doing, and occasionally an update can introduce a bug of its own. Pretending those inconveniences do not exist would make security advice less credible, not more.
The more useful comparison is between the inconvenience of maintaining software and the consequences of leaving known weaknesses uncorrected indefinitely.
When a vendor identifies a security problem and releases a patch, a solution has already made most of the journey from researcher to developer to update server. The final step is unusually ordinary: the corrected software has to reach the device you are actually using.
Automatic updates can handle much of that work quietly. Notifications cover the cases that still require a decision. Restart scheduling can reduce disruption, and supported software gives vendors an ongoing path to correct newly discovered problems.
Seen that way, an update is not simply a company asking to change your device again. Quite often, it is evidence that someone discovered something worth fixing — and that the correction is waiting for permission to become part of the software you rely on.
Alex Carter is a technology writer with five years of experience in the tech field. He now focuses on creating clear, practical articles that help beginners in the United States better understand computers, smartphones, online services, and everyday digital technology.