Public Wi-Fi has accumulated a reputation that is difficult to shake. For years, people were warned not to check email at airports, sign in to accounts from coffee shops, or do anything remotely sensitive on hotel networks because someone nearby might be able to intercept whatever they were doing. That advice was not invented out of nowhere; older websites frequently transmitted information without the encryption that is commonplace today, which made an open wireless network a considerably more uncomfortable place to enter passwords or personal information.
The internet has changed, however, and public Wi-Fi deserves a more nuanced explanation than “never use it.”
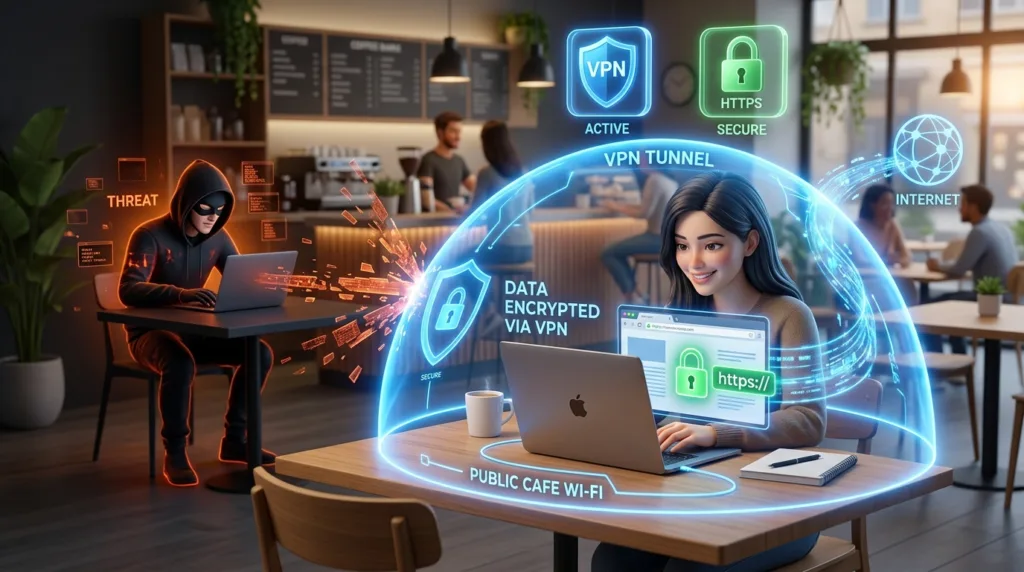
Most mainstream websites now use HTTPS, which encrypts the information traveling between your browser and the website. As the Federal Trade Commission explains in its current public Wi-Fi guidance, widespread website encryption means that using a public Wi-Fi network is generally safer today than it was in the early years of widespread wireless internet access. That does not make every hotspot trustworthy, nor does it mean you can disregard browser warnings, connect to whatever network name appears first, and enter sensitive information anywhere you please.
The practical question is no longer simply whether public Wi-Fi is “safe” or “unsafe.” It is whether you understand which parts of the connection are protected, which risks remain, and when an ordinary convenience is not worth introducing unnecessary uncertainty.
The network and the website protect different parts of the journey
When you visit a website, information travels from your device through the network you are using and eventually reaches the service you requested. On a home connection, that network may be your own Wi-Fi router. At an airport, hotel, restaurant, or library, you are relying on infrastructure controlled by someone else.
HTTPS protects an important part of that exchange by encrypting the connection between your browser and the website. In practical terms, if you are connected to an ordinary public hotspot and visit a properly configured HTTPS website, another person on the same wireless network should not simply be able to read the contents of your password, messages, or other encrypted traffic as though they were looking over your shoulder.
This distinction explains why some older public Wi-Fi advice now sounds more dramatic than current consumer guidance. The FTC explicitly notes that because most websites now encrypt their connections, public Wi-Fi is usually much safer than it once was. Google Chrome likewise explains that HTTPS protects information traveling between the browser and the site, while warning users when a connection is not private. Google’s guide to checking whether a site’s connection is secure is useful for understanding what those browser indicators actually mean.
Encryption does not, however, certify the honesty of the destination itself. A fraudulent website can use HTTPS too. Your connection to the scammer may be encrypted perfectly while the scammer still receives every password or credit card number you voluntarily submit. The lock or secure-connection indicator therefore answers one question — whether the connection is encrypted — but it does not answer another equally important one: whether you are on the correct website.
That is the same distinction we discussed in How to Recognize a Phishing Email Before You Click. Technical protection and human judgment solve different parts of the problem.
The network name itself deserves more attention than most people give it
Imagine sitting in an airport and opening the Wi-Fi menu on your laptop. Several networks appear:
Airport_Free_WiFi
Airport Guest
Free_Airport_WiFi
Terminal_WiFi
Without additional information, which one actually belongs to the airport?
A malicious hotspot does not need sophisticated technology to create confusion if users are willing to connect based only on a plausible-looking name. Someone can configure a wireless network whose name resembles the legitimate network and wait for nearby devices to connect.
This is why the Cybersecurity and Infrastructure Security Agency recommends confirming the correct public network name and login procedure with the organization providing it rather than assuming that the most convincing-looking network is legitimate. In a hotel, that might mean checking the information provided at reception; in a coffee shop, it might mean asking an employee; at an airport, official signage or the airport’s own instructions may identify the network.
The habit is simple, but the reasoning behind it is important. When you connect to someone else’s wireless network, you are accepting their infrastructure as part of the route your device uses to reach the internet. Verifying the network before connecting reduces the possibility that you have joined an imitation hotspot created specifically to attract people who are not paying attention.
That does not mean you need to interrogate an employee every time you order coffee and open a laptop. If the venue clearly displays the network name and connection instructions, that may be all the confirmation you need. The point is to avoid treating a network name as proof merely because it contains the name of the place where you happen to be sitting.
A password on the café wall does not turn the network into your home Wi-Fi
Another common assumption is that a public network must be secure because it requires a password.
A password can be useful, particularly when the network uses modern wireless encryption, but the existence of a password does not transform a shared hotspot into a private environment. If the same password is printed on a menu, handed to every hotel guest, or displayed beside the cash register, then many people you do not know can legitimately join that network.
That is fundamentally different from a home network whose password is known only to members of the household and trusted visitors.
For an everyday user, the more useful distinction is not “password versus no password” but trusted private network versus shared network. A hotel connection can be legitimate, properly configured, and perfectly reasonable to use while still being a network shared with dozens or hundreds of other guests. You should continue relying on encrypted websites, current software, sensible account security, and the same skepticism you would use elsewhere online.
Public Wi-Fi is therefore not a magical danger zone, but neither is the password printed on your room key a security certificate for everything you do once connected.
Some activities deserve a higher threshold of confidence
Checking a restaurant menu or reading a news article does not carry the same consequences as transferring money or changing the password on your primary email account.
This is where public Wi-Fi safety becomes a matter of proportion rather than prohibition.
If you are connected to the verified Wi-Fi network at a major airport, your browser shows a secure connection, and you want to read ordinary websites while waiting for a flight, there is little reason to behave as though the internet has become unusable. Conversely, if you are about to access a particularly sensitive account and your phone has a reliable cellular connection available, using mobile data may eliminate one source of uncertainty for very little inconvenience.
Mobile data is not magically invulnerable either, but it allows you to avoid relying on the local public hotspot altogether. For a quick banking session, an important password change, or access to highly sensitive work systems, that can be a sensible trade.
The decision becomes even clearer when something about the public network feels questionable. Perhaps you cannot verify its name, the connection repeatedly redirects you to unfamiliar pages, or the browser displays a warning you do not understand. There is no obligation to solve the mystery while sitting in an airport terminal. Disconnecting and using cellular data — or waiting until you reach a network you trust — is often the easiest answer.
Security is easier when you allow inconvenience to influence the decision realistically. Spending thirty seconds switching networks may be worthwhile for a consequential task; refusing to use public Wi-Fi for anything whatsoever can be unnecessarily restrictive.
Browser warnings should interrupt your routine
Modern browsers do a substantial amount of security work quietly, which creates a peculiar problem: users become so accustomed to clicking through ordinary screens that warnings can start to feel like obstacles rather than information.
If Chrome, Safari, Edge, Firefox, or another browser tells you that a connection is not private, that a certificate has a problem, or that a site may be dangerous, do not automatically search for the button that lets you continue.
The warning may have an innocent explanation. A website can be misconfigured, a hotel’s Wi-Fi login system can behave awkwardly, or a device’s clock can cause certificate problems. Even so, entering passwords or sensitive information while the browser is explicitly telling you that it cannot establish the expected secure connection is a poor moment to assume everything is fine.
Google’s Chrome documentation distinguishes between encrypted connections and pages where the browser cannot establish a private connection, advising users not to enter personal information on sites marked as unsafe. That is useful guidance well beyond Chrome itself: security warnings are most valuable when they change your behavior.
If a familiar site unexpectedly produces a certificate or privacy warning only while you are on one particular public network, switching to mobile data and checking again can also help distinguish a website problem from something associated with the connection you are using.
Automatic connection is convenient until your device remembers too much
Phones and laptops are designed to make connectivity effortless. After joining a network once, a device may remember it and reconnect later without requiring much attention from you.
At home, that is exactly what you want.
With public networks, automatic reconnection can become less useful, particularly when you visit many hotels, airports, conference centers, cafés, or other shared locations over time. Your device can accumulate a long history of remembered networks whose names are no longer meaningful to you.
Removing public networks you no longer use is therefore a reasonable housekeeping habit. You do not need to obsessively delete a hotspot immediately after leaving every café, but there is little value in carrying years of forgotten wireless profiles either.
The exact controls differ among Windows, macOS, Android, and iOS, yet all major platforms provide ways to forget saved networks or adjust connection behavior. If you are unfamiliar with the broader way devices manage wireless connections, the later article How to Connect Your Phone to Wi-Fi and Mobile Hotspots will cover the everyday mechanics from the smartphone side.
Another related habit is turning off file-sharing or device-discovery features when you do not need them on shared networks. Modern operating systems often distinguish between public and private network profiles precisely because a computer that should be easily discoverable by devices inside your home may not need the same visibility in an airport lounge.
Updates matter more than security folklore
Public Wi-Fi advice sometimes becomes focused on elaborate precautions while overlooking simpler protections that matter every day, regardless of which network you use.
An outdated browser, operating system, or application may contain vulnerabilities that have already been corrected in newer versions. Keeping devices reasonably current therefore contributes more to practical security than memorizing a collection of dramatic rules about coffee-shop hotspots.
The FTC recommends keeping operating systems, browsers, security software, and phones updated as part of its current public Wi-Fi guidance. Automatic updates are particularly useful for ordinary users because they reduce the likelihood that important fixes are postponed indefinitely.
This is also why Why Software Updates Matter for Your Digital Security belongs in the same security cluster. The quality of the network is only one layer. The device connecting to it and the software interpreting online content matter as well.
Strong, unique passwords and two-factor authentication provide another layer. If a password is somehow obtained, What Is Two-Factor Authentication and Why Should You Use It? explains why an independent authentication factor can make that credential considerably less useful to an attacker.
None of these measures needs to carry the entire burden. Security becomes more resilient when several ordinary protections overlap.
Where does a VPN fit into all of this?
Virtual private networks, or VPNs, are frequently presented as mandatory equipment for anyone who uses public Wi-Fi. The reality is more contextual.
A VPN creates an encrypted connection between your device and the VPN provider’s infrastructure, which can protect traffic across the local network and change which intermediary is able to observe parts of your connection. Businesses also use VPNs to provide employees with controlled access to internal systems from outside the office.
What a VPN does not do is make fraudulent websites trustworthy, prevent you from entering a password into a phishing page, or automatically protect an account with weak credentials. It also shifts some trust from the local network to the VPN provider, which makes the quality and privacy practices of that provider relevant.
For an organization that requires a corporate VPN before employees access internal resources, the decision is straightforward: follow the organization’s security policy. For an ordinary user browsing HTTPS websites on a verified public hotspot, the FTC’s current guidance is notably less alarmist than older advice because widespread encryption already protects much of normal web traffic.
A VPN can still be useful in particular circumstances, but “public Wi-Fi exists” is not enough information by itself to determine whether you need one. The question should be what you are trying to protect, which network you are using, and whether you trust the VPN service more than the infrastructure it is replacing as an intermediary.
That is a healthier way to evaluate security tools than assuming that installing one product removes the need for judgment.
Public Wi-Fi is safest when it stops feeling exceptional
There is a temptation in digital security to divide the world into safe places and dangerous places: home Wi-Fi is safe, airport Wi-Fi is dangerous; an HTTPS page is safe, a page without the familiar indicator is dangerous; a password-protected network is safe, an open one is not.
Reality is less tidy.
A fraudulent website can be reached from your perfectly secured home network. A legitimate HTTPS website can function normally from a public airport hotspot. A password-protected café network can still be shared by hundreds of strangers, while a cellular connection may provide a simpler alternative when you are handling something unusually sensitive.
The better habit is to think in layers. Verify that the network you intend to join is actually the one provided by the venue. Pay attention to browser security warnings rather than clicking through them automatically. Prefer encrypted websites, keep devices updated, use strong account protections, and reserve a more trusted connection for activities whose consequences justify the extra caution.
Once those habits become ordinary, public Wi-Fi becomes less dramatic.
You do not need to assume that opening your laptop in a coffee shop places every account in immediate danger, nor do you need to treat a familiar network name and an HTTPS lock as permission to stop paying attention. What matters is understanding which protections are already working for you, recognizing where their limits are, and making a different choice when the situation carries enough risk to justify it.
That is a more durable form of digital safety than simply memorizing that one type of network is “good” and another is “bad.”
Alex Carter is a technology writer with five years of experience in the tech field. He now focuses on creating clear, practical articles that help beginners in the United States better understand computers, smartphones, online services, and everyday digital technology.