You visit a website because you want to read an article, check a store’s hours, or look up a recipe, and before you have done any of those things, a banner appears across the screen.
Accept all cookies.
Perhaps there is also a smaller button labeled Manage preferences, Reject non-essential cookies, or something similarly uninviting. After seeing versions of the same message hundreds of times, it is understandable that many people simply choose whichever button makes the banner disappear fastest.
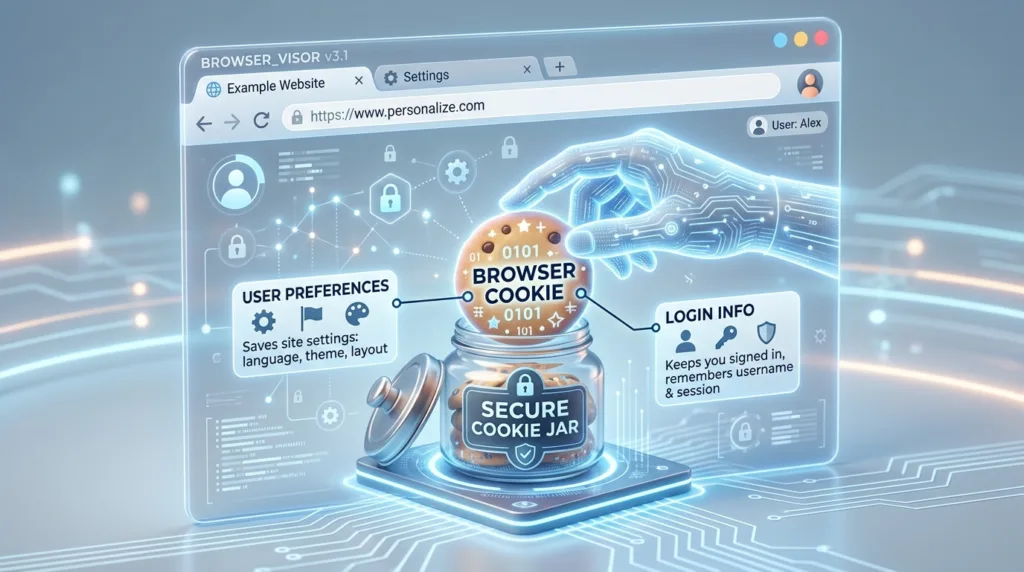
What makes that decision confusing is that the word cookie covers several different purposes. Some cookies help a website remember that you signed in or selected English instead of Spanish. Others can be involved in analytics, advertising, or recognizing activity across different websites. Treating all of them as either harmless conveniences or dangerous tracking tools misses what is actually happening.
A browser cookie is essentially information that a website asks your browser to store and return later. Mozilla’s explanation of browser cookies gives familiar examples: cookies can remember login status, language choices, location preferences, and other information that allows a website to recognize something about a previous visit.
The more useful question, therefore, is not simply whether cookies are good or bad. It is what a particular cookie is being used for, who can use it, and whether you need to agree to every optional purpose in order to use the website normally.
What happens when a website “remembers” you
Imagine signing in to an online store, adding two products to your cart, opening another page, and then returning to the cart. The products are still there. You did not type your name again, explain which items you had selected, or rebuild the session from the beginning; the website maintained enough information to connect one request with the next.
Cookies are one of the mechanisms that make experiences like this possible.
The web would be considerably more cumbersome if every page behaved as though it had never seen you before. A website might forget your chosen language each time you moved to another section, require repeated sign-ins, or lose temporary information needed to complete a task. In that sense, cookies are not an accidental addition to browsing. They help websites preserve continuity across interactions that would otherwise be disconnected.
Google’s Chrome documentation on cookies describes the same practical role: websites can use cookies to keep users signed in, remember preferences, and provide content relevant to a visitor’s settings or location.
That functionality explains why blocking every cookie indiscriminately can occasionally make a website behave strangely. The login may not persist, a preference may disappear, or some embedded feature may stop working because the browser is refusing information the site expected to store.
At the same time, remembering your language and remembering enough about your browsing behavior to build an advertising profile are not equivalent uses. This is where the conversation moves from basic functionality into privacy.
“First-party” and “third-party” describe a relationship, not whether a cookie is automatically safe
The terminology sounds technical, but the underlying distinction is fairly intuitive.
A first-party cookie comes from the website you are visiting. If you are on example.com and that site stores information needed to keep your session active or remember a preference, that is the kind of direct relationship usually described as first-party.
A third-party cookie is associated with another organization whose content or technology is present on the page. A website can include advertising systems, analytics services, embedded media, social features, or other resources supplied by outside companies, and those third parties may historically have been able to recognize a browser across multiple websites using their own cookies.
Google explains this distinction in its Chrome cookie documentation, noting that first-party cookies are created by the site shown in the address bar, whereas third-party cookies originate from other sites whose content may be embedded in the page.
This does not mean that every first-party cookie deserves unlimited trust or that every third-party interaction is malicious. The categories describe who is setting or using the cookie in relation to the site you intentionally visited. Privacy concerns become more pronounced when information can be used to connect activity across unrelated websites, because the resulting picture can reveal far more about someone’s browsing behavior than any individual page would show on its own.
Mozilla has made cross-site tracking a major focus of Firefox’s privacy protections. Its current Total Cookie Protection explanation describes an approach that limits the ability of cookies to follow a user from one website to another by isolating them according to the site where they were created.
This broader shift in browser design is worth noting because cookie privacy is no longer controlled solely by whatever button you choose on an individual banner. Browsers themselves increasingly impose restrictions on certain forms of cross-site tracking.
So what are you agreeing to when you press “Accept All”?
There is no universal answer because cookie banners are not standardized menus with identical choices.
On one website, accepting all may allow basic site functionality plus audience measurement. On another, the same button may authorize a much broader collection of advertising, personalization, analytics, or partner technologies. The categories, terminology, and number of companies involved can vary dramatically.
That is why the words Accept All should be read literally: you are generally agreeing to everything covered by the site’s presented consent options, not merely giving the website permission to remember that you logged in.
When a site offers a Reject non-essential option, it may allow the website to continue using cookies or similar storage mechanisms considered necessary for the service while declining optional categories. A preferences panel may go further and let you make distinctions among analytics, advertising, personalization, and other purposes.
For a reader who simply wants a practical default, there is no obligation to accept every optional cookie merely because a website displays a banner. If the site offers a straightforward way to reject non-essential purposes and you do not want the additional tracking or personalization, choosing that option is entirely reasonable.
There is also no reason to panic if you have pressed Accept All on hundreds of websites in the past. Cookie consent is not an irreversible decision made once for the life of the computer. Browsers provide tools to remove stored site data, restrict categories of cookies, and change how websites are allowed to use them in the future.
Cookies do not contain a miniature copy of everything on your computer
The word tracking can make cookies sound as though a website has gained broad access to the device itself. That is not how ordinary browser cookies work.
Mozilla notes that websites cannot use cookies to access arbitrary files on your computer, and a site cannot magically place information into a cookie that you never provided or that the browsing interaction did not generate. Cookies exist within the browser’s web-storage environment and are governed by rules about which sites are allowed to receive them.
They can nevertheless contain or be associated with information that becomes privacy-relevant. A cookie might contain an identifier that allows a service to recognize the same browser later, for example, and that identifier can be connected on the service’s side with other information about account activity or browsing behavior.
That distinction matters because it avoids two misleading extremes. Cookies are not tiny pieces of malware rummaging through your hard drive, but neither are they meaningless text files that can never contribute to tracking.
Their significance depends on the information they represent and how that information is combined elsewhere.
This is similar to many other privacy decisions we have discussed in Vandutz: the technology itself usually needs context. In How to Check and Change App Privacy Permissions, camera or location access was not automatically good or bad; the question was whether the permission matched the feature. With cookies, the comparable question is what information is being retained and for what purpose.
Deleting cookies can solve one problem while creating several small inconveniences
People often discover the Clear cookies option while troubleshooting a website and understandably wonder whether they should use it regularly.
Deleting cookies is not inherently harmful, but it changes what websites remember about your browser. Google warns in its Chrome documentation that removing cookies can sign you out of websites and erase saved site preferences, which explains why a browser can feel strangely unfamiliar immediately after a large cleanup.
Suppose you delete all cookies this afternoon. The next time you visit several services, you may need to sign in again. Sites can ask for your language or location preference again, cookie banners themselves may return because the site’s record of your previous choice is gone, and shopping carts that depended on locally stored session information may be empty.
None of those outcomes means anything was damaged. You deliberately removed information websites had been using to recognize previous visits.
Clearing cookies can be useful when a particular website behaves incorrectly, when you are troubleshooting a sign-in problem, when you want to remove stored site information from a shared computer, or when you simply want to reduce accumulated browsing data. What is less useful is treating cookie deletion as a ritual that must happen constantly regardless of context.
Privacy controls work better when you know what outcome you are trying to achieve.
Blocking third-party cookies is different from disabling cookies entirely
This distinction has become increasingly relevant because modern browsers provide more granular privacy controls than the simple “cookies on / cookies off” model people may remember.
Chrome, for example, provides settings specifically for third-party cookies and warns that blocking them can sometimes cause websites that rely on third-party functionality to behave differently. Firefox goes further with Enhanced Tracking Protection and Total Cookie Protection, which are designed to restrict cross-site tracking while trying to preserve ordinary website functionality.
That direction reflects a broader reality: many of the privacy concerns associated with cookies involve cross-site recognition rather than the fact that a website can remember its own login session.
For a beginner, this means you generally do not need to search for a master switch that prevents every website from storing anything. The privacy settings already available in your browser may provide more targeted controls, and browsers continue to evolve how they handle tracking technologies.
If changing a privacy setting causes one particular website to stop working correctly, you can investigate that site rather than abandoning every browser protection at once. Mozilla explicitly acknowledges that stronger cookie isolation can occasionally break site functionality and provides per-site troubleshooting options for those cases.
The useful principle is incremental adjustment: change the smallest setting necessary to solve the actual problem.
Cookie banners are only one part of online tracking
It is easy to come away from repeated consent banners with the impression that cookies are synonymous with online privacy.
They are not.
Websites and advertising systems can use other technologies and signals to measure activity, identify sessions, prevent fraud, personalize services, or attempt to recognize users and devices. Removing one cookie therefore does not guarantee that a website knows nothing about your visit, just as accepting a cookie does not necessarily mean every possible type of tracking has suddenly been enabled.
This matters because privacy advice becomes misleading when it reduces a complex ecosystem to one browser setting.
For most everyday users, there is no need to understand every tracking technology used on the modern web. A more realistic approach is to combine several understandable choices: keep the browser current, use its built-in privacy protections, be selective when websites offer meaningful consent choices, limit unnecessary account and app permissions, and pay attention to the websites where you provide personally identifying information.
The same broader perspective applies to private browsing. Incognito or private mode affects what the browser stores locally during a particular session, but it does not make someone invisible to websites, internet providers, employers, or every other participant in the connection. We will examine that misconception separately in What Is Incognito Mode and What Does It Actually Do?.
Understanding those boundaries is more useful than searching for one privacy button that supposedly solves everything.
What should you do the next time a cookie banner appears?
You do not need to conduct a privacy audit every time you want to read a webpage.
If the site gives you a clear choice between accepting everything and rejecting non-essential cookies, choosing the more limited option is a sensible default when you do not want optional advertising or tracking technologies. If you use the site frequently and value certain personalization features, you may decide differently.
When a preferences panel appears, glance at the categories rather than assuming they all describe the same kind of activity. Necessary cookies that keep a service functioning are conceptually different from advertising or cross-site tracking technologies, even if the banner places them together under the general word cookies.
On a trusted site that you use regularly, accepting some optional preferences may be perfectly reasonable. On a website you intend to visit once for thirty seconds, there may be little personal benefit in granting broad optional tracking permissions simply to make the banner disappear.
The decision does not need to become ideological. You are not choosing whether cookies should exist; you are deciding how much information a particular browsing interaction needs to retain.
That small reframing makes the endless parade of cookie banners considerably easier to interpret. Instead of seeing Accept as the button required to enter the website, you can recognize it as one of several possible privacy choices and, when alternatives are available, choose the one that better matches what you actually want from the visit.
Alex Carter is a technology writer with five years of experience in the tech field. He now focuses on creating clear, practical articles that help beginners in the United States better understand computers, smartphones, online services, and everyday digital technology.